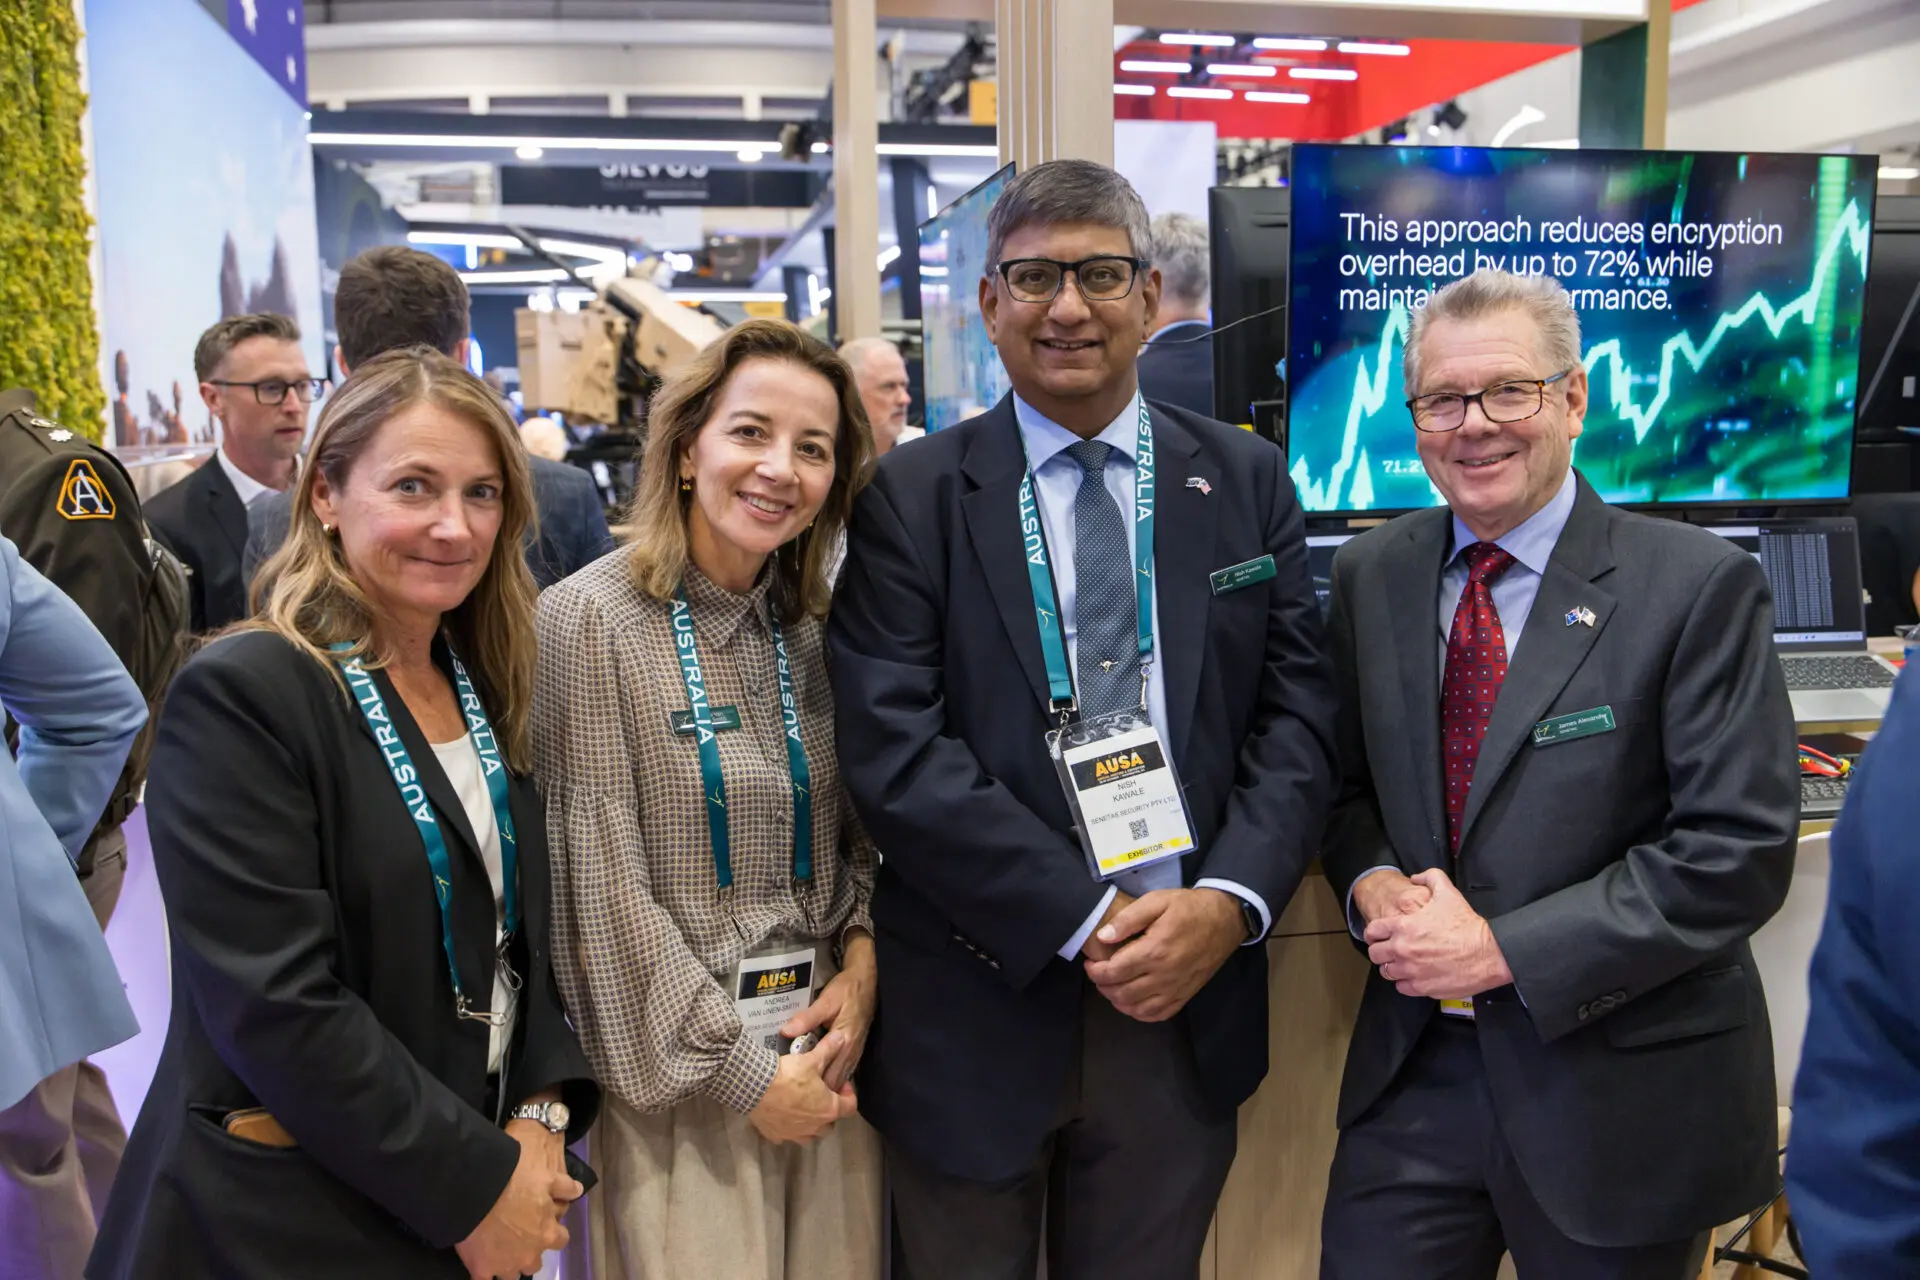
The U.S. Army signaled a rapid acceleration in autonomous systems adoption by redesignating Futures and Concepts Command as the Army Futures and Autonomous Systems Command (FASCOM) at AUSA 2026 in Washington DC. Conversations across the three-day event centered on autonomous systems, artificial intelligence and the urgent need for post-quantum cryptography, resilient communications, and command and control.
This shift in focus comes as SpaceX recently imposed speed limits on Starlink terminals in motion in Ukraine, demonstrating the vulnerabilities of relying on externally controlled infrastructure for defense; as Senetas Chief Marketing Officer Andrea Van Unen-Smith observes, “defence technology is being adopted faster than ever, and the security foundations underneath it must keep pace.”
Senetas PQC Mandate Accelerates Post-Quantum Transition
Senetas, an Australian defence technology company exhibiting at the event, noted a strong focus on post-quantum cryptography as a critical component of this evolving landscape. Ukrainian officials reported that subsequent restrictions on the militarised version, Starshield, affecting equipment exceeding 161 km/h, impacted interceptor drone operations. This incident highlighted a key takeaway for defence organisations: capability built on infrastructure they do not control can be altered unexpectedly, necessitating encryption solutions that remain under operator control and can adapt to changing conditions.
The need for cryptographic agility, the ability to update algorithms and security controls without overhauling entire networks, was a recurring theme, particularly given the coexistence of new platforms with legacy infrastructure. Senetas observed that defence modernisation efforts require integration of newer command-and-control technologies into existing communications systems, presenting significant challenges.
The company emphasized that cryptography cannot remain static while surrounding technologies evolve, and that defence organisations must proactively prepare for the transition to post-quantum cryptography (PQC) to maintain security and compliance. Senetas’ government mandate requires federal agencies to transition high-value assets and high-impact systems to PQC in two phases: PQC for key establishment by December 31, 2030, and PQC for digital signatures by December 31, 2031.
The Department of Defense’s Post-Quantum Cryptography Strategy mirrors this timeline, requiring all systems to support PQC or be phased out by the end of 2030, with full PQC implementation mandated by the end of 2031, unless otherwise specified. This aggressive schedule is further reinforced by the National Institute of Standards and Technology (NIST), which recently published its final transition report, NIST IR 8547, deprecating RSA and elliptic curve cryptography at all key sizes after 2030 and disallowing their use after 2035.
The urgency extends beyond the anticipated arrival of a cryptographically relevant quantum computer. The true deadline is dictated by the lifespan of encrypted data. Much of the network equipment currently in service is expected to remain operational well into the post-quantum era, making proactive preparation essential for maintaining security and compliance beyond 2030. Visitors to Senetas’ booth at AUSA 2026 consistently inquired about the practical implications of the PQC migration mandate and the necessary steps to prepare.
The company’s assessment is that for defence networks with extended operational lifecycles, immediate action is necessary to ensure both compliance and sustained security in the face of the evolving quantum threat. “The US post-quantum timeline is now set,” according to the company, and the time to begin the transition is now.
See today’s quantum computing news on Quantum Zeitgeist for the latest breakthroughs in qubits, hardware, algorithms, and industry deals.