
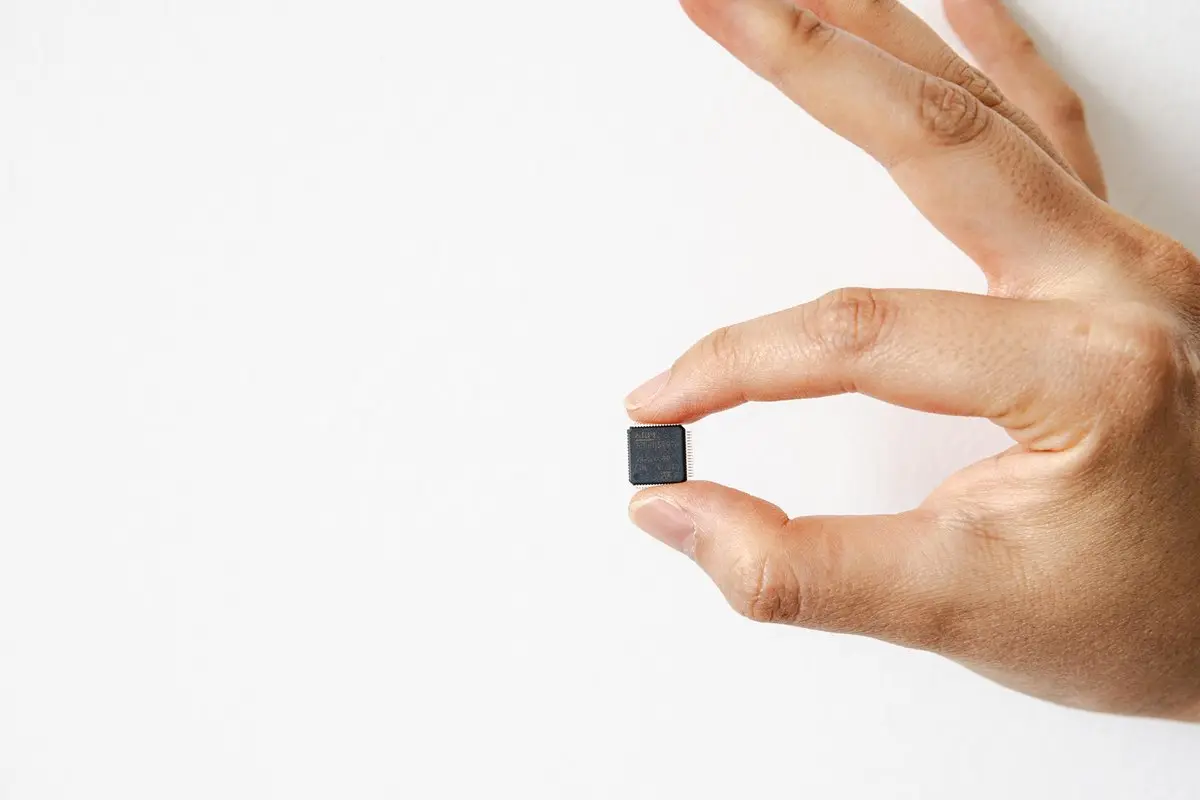
Sixty-four metal pins extend from a chip barely larger than a fingernail, a stark reminder of the physical complexity, and potential attack surface, hidden within modern electronics. Researchers at the Max Planck Institute for Security and Privacy are developing methods to detect hardware tampering and build chips resistant to both physical manipulation and future quantum attacks. The team uses open-source software, HAL, to analyze chip schematics and is proactively enhancing open-source chips with quantum-secure circuits. “Manipulation deep within a chip would be almost impossible to detect – and could threaten entire infrastructures.”
HAL Software Detects Hardware Trojans in Chip Designs
This capability is particularly vital in detecting hardware Trojans, circuits intentionally embedded to create security vulnerabilities and compromise data integrity, a standard scenario in related research. While HAL does not function as a fully automated vulnerability scanner due to the sheer variety of potential Trojan designs, it effectively narrows the search for analysts, highlighting areas of interest within a complex chip layout.
The software’s utility extends beyond academic research, attracting interest from government research laboratories and agencies, as well as companies focused on security-critical applications. “Most HAL users are companies working in security-related fields,” explains Julian Speith, a postdoctoral researcher involved in the software’s development, indicating a practical demand for tools that can proactively assess chip trustworthiness.
This level of scrutiny is becoming increasingly important given the concentration of chip manufacturing in a limited number of global locations. Pretty much all circuits that surround us, as well as our entire digital wireless infrastructure, rely on chips made in Taiwan, China, South Korea or, to a small extent, the USA. Beyond Trojan detection, the institute is also proactively fortifying chip designs against future threats, specifically those posed by quantum computers. Researchers are enhancing open-source chips with quantum-secure circuits, employing encryption methods designed to withstand attacks from these powerful, yet-to-be-fully-realized machines.
Every Pavona chip manufactured on this basis in the future will automatically include these circuits, ensuring post-quantum cryptography runs efficiently. This approach represents a shift towards building security directly into the hardware, rather than relying solely on software updates to address vulnerabilities. The team’s work acknowledges the inherent difficulties in visually inspecting chip designs for tampering, as transistors often appear identical in images, making it challenging to discern their function based solely on physical appearance.
Even with detailed connection maps, determining the purpose of specific chip areas remains a complex task without accompanying documentation. HAL provides an analytical layer, assisting experts in interpreting the detailed web of connections and identifying anomalies.
For example, when a certification body receives a cellular base station or a smartphone chip, it can investigate whether the chip can be put into a state, using a specific input, in which it suddenly reacts differently from how it is supposed to.
Christof Paar, who heads the Embedded Security group at the Max Planck Institute for Security and Privacy in Bochum
Reconstructing Netlists Reveals Hidden Chip Tampering
Reconstructing a chip’s netlist, the detailed map of its internal connections, is proving essential for uncovering subtle hardware tampering, a process that can introduce vulnerabilities undetectable through software-based security measures. To validate HAL’s capabilities, the institute’s developers intentionally introduced a hidden signal wire into a virtual chip design, a component designed to leak a cryptographic key under specific conditions. “If attackers know how to activate this function, they can simply read the key via the output,” explained Julian Speith, highlighting the potential for covert data exfiltration.
The institute’s concerns extend beyond detecting existing tampering to proactively fortifying future chip designs. The team is actively integrating quantum-secure circuits into open-source chips, creating hardware that can resist attacks from increasingly powerful quantum computers. “Quantum computers pose a threat to end-to-end encryption in messaging services and security measures used in online financial transactions, for example,” demonstrating the urgency of this preventative approach.
This isn’t merely a theoretical exercise; the team anticipates a critical juncture in quantum computing’s development. “It will be a long-awaited milestone, and we are already very well-prepared for it,” they state, suggesting a proactive stance against a future threat. The potential for malicious actors to exploit hardware vulnerabilities is not limited to theoretical scenarios. The institute points to the possibility of nation-state actors embedding into chips, enabling them to remotely disable critical infrastructure.
“In theory, a manufacturer like Huawei in China could build a ‘kill switch’ into its chips and then use a secret command to shut down all cell towers with Huawei hardware in Germany,” a stark illustration of the geopolitical implications of compromised hardware. While HAL currently focuses on identifying these hidden functions within reconstructed netlists, the ultimate goal is to build security directly into the chip’s design, making tampering significantly more difficult and detectable.
Quantum computers pose a threat to end-to-end encryption in messaging services and security measures used in online financial transactions, for example.
Hoang Nguyen Hien Pham, doctoral researcher in the Cryptographic Engineering Group of Peter Schwabe at the Max Planck Institute for Security and Privacy
Quantum-Secure Circuits Enhance Chip Encryption
Minimizing both cost and development time, the team’s approach centers on adapting existing chip designs rather than creating entirely new ones. Developing entirely new chips would be an immense undertaking, demanding resources far beyond the scope of most research groups, but Pham and her colleagues are focused on modifying current security chips to meet future demands with minimal changes. “We are simply adding a few new instructions to an existing chip,” Pham explains, outlining a method that allows circuits to support both conventional and quantum-resistant cryptographic algorithms during the transition to a post-quantum world.
This adaptation relies heavily on OpenTitan, an open-source chip whose internal workings are publicly accessible, enabling thorough review and enhancement by companies and independent experts. The Max Planck Institute team has integrated their quantum-secure circuits into Pavona, a new project built upon the OpenTitan foundation.
The institute suggests that relying on post-quantum cryptography now, and ideally using open-source technology is the most prudent course of action. “It’s better to rely on post-quantum cryptography now, and ideally on open-source technology,” they state, advocating for a collaborative and transparent approach to security. The complexity of analyzing chip circuitry is considerable; reconstructing the layers of metal traces connecting transistors is likened to assembling a map from numerous small photographs. This process, while challenging, is essential for understanding how a chip functions and identifying potential vulnerabilities.
Pretty much all circuits that surround us, as well as our entire digital wireless infrastructure, rely on chips made in Taiwan, China, South Korea or, to a small extent, the USA.
Christof Paar, who heads the Embedded Security group at the Max Planck Institute for Security and Privacy in Bochum
Supply Chain Reliance Creates Hardware Vulnerabilities
The increasing complexity of chip design necessitates new approaches to verification, as even seemingly straightforward functions can obscure hidden vulnerabilities. This reconstruction allows analysts to pinpoint areas requiring closer scrutiny, though definitive assessment of a vulnerability still requires human expertise. These Trojans, intentionally embedded circuits, represent a significant threat because they can grant unauthorized access or exfiltrate confidential data, and their detection relies on understanding the chip’s intended functionality versus its actual behavior.
The challenge lies in the sheer number of potential Trojan implementations, preventing fully automated scanning and requiring analysts to focus on areas flagged by HAL. Transistors appear identical in imagery, making functional determination from connections alone a complex task. Manufacturers rarely provide detailed documentation outlining chip functions, further complicating the analysis process and highlighting the need for reverse engineering tools like HAL.
This reliance on reconstruction emphasises the vulnerability inherent in complex supply chains, where verifying the integrity of components becomes increasingly difficult as designs are outsourced and manufacturing processes become more opaque. Openness, according to the researchers, is paramount to building trust in hardware security. This approach contrasts with proprietary designs, where security relies on secrecy, a strategy that becomes less effective as reverse engineering tools become more sophisticated.
The team is actively applying this principle by developing open-source chips enhanced with quantum-secure circuits, providing a transparent foundation for future hardware security. The integration of these quantum-secure circuits isn’t simply a future-proofing measure. It’s a proactive step toward mitigating the risks posed by increasingly powerful computing capabilities. The team’s work also addresses the potential for malicious manipulation during manufacturing, citing a scenario where a manufacturer could embed a “kill switch” into chips, allowing remote shutdown of critical infrastructure.
This highlights the need for robust verification processes throughout the entire supply chain, from design to fabrication. The team’s methodology acknowledges that complete automation of vulnerability detection is unrealistic, but HAL’s ability to narrow the search area significantly reduces the workload for security analysts. By focusing on reconstructed netlists, the software helps analysts understand the chip’s intended behavior and identify deviations that could indicate malicious intent. This combination of automated analysis and human expertise represents a pragmatic approach to addressing the growing threat of hardware tampering and ensuring the integrity of critical systems.
In theory, a manufacturer like Huawei in China could build a ‘kill switch’ into its chips and then use a secret command to shut down all cell towers with Huawei hardware in Germany.
Christof Paar, who heads the Embedded Security group at the Max Planck Institute for Security and Privacy in Bochum
Physical Chip Analysis Identifies Anomalous Behavior
The reconstruction of a chip’s circuit diagram, known as a netlist, demands painstaking work even for smaller components like those found in bank cards, a process refined over many years of practical application. While physically opening these chips is established practice, determining the function of identical-looking transistors remains a significant hurdle, as manufacturer-specific hardware lacks accompanying documentation detailing operational areas. These chips use “gates”, specific transistor connections that perform logical operations, as fundamental building blocks, allowing researchers to trace signal pathways and understand the chip’s intended behavior.
The open-source software HAL analyzes reconstructed chip schematics known as netlists, and identifies possible hardware Trojans, which are additional circuits that create security vulnerabilities. Each layer demands thousands of individual images at high resolution, demonstrating the intricacy of modern microelectronics and the scale of the reconstruction task.
However, even a complete netlist is insufficient for understanding a chip’s functionality. It lacks the necessary labels and explanations to identify the purpose of individual circuits. “While the netlist contains information on the individual transistors and their connections, it still lacks any labels or explanations as to which functions they perform,” explains the institute, highlighting the need for further analysis to map circuit elements to specific operations.
This approach contrasts sharply with relying solely on detecting anomalies in an entirely opaque design, where even subtle alterations can be difficult to discern. Dust and scratches on the chip’s surface can obscure or misrepresent transistors in the images, requiring careful manual review to ensure accuracy. “Even a tiny speck of dust or a scratch on the surface can cause some of the transistors in an image to be obscured or misinterpreted,” notes the institute, emphasising the challenges of physical analysis.
The team’s work builds on the understanding that software updates are insufficient to address deeply embedded hardware manipulation, as “Software can be updated,” but physical alterations remain persistent and difficult to detect. The team’s goal is to provide tools and techniques that allow for more thorough and reliable hardware verification, ultimately enhancing the security of critical infrastructure and protecting against increasingly sophisticated attacks.
Anyone who wants to manipulate a chip ultimately has to replace or modify certain gates – and it is precisely this process that has to be made as difficult as possible through clever design.
Christof Paar, who heads the Embedded Security group at the Max Planck Institute for Security and Privacy in Bochum
See today’s quantum computing news on Quantum Zeitgeist for the latest breakthroughs in qubits, hardware, algorithms, and industry deals.