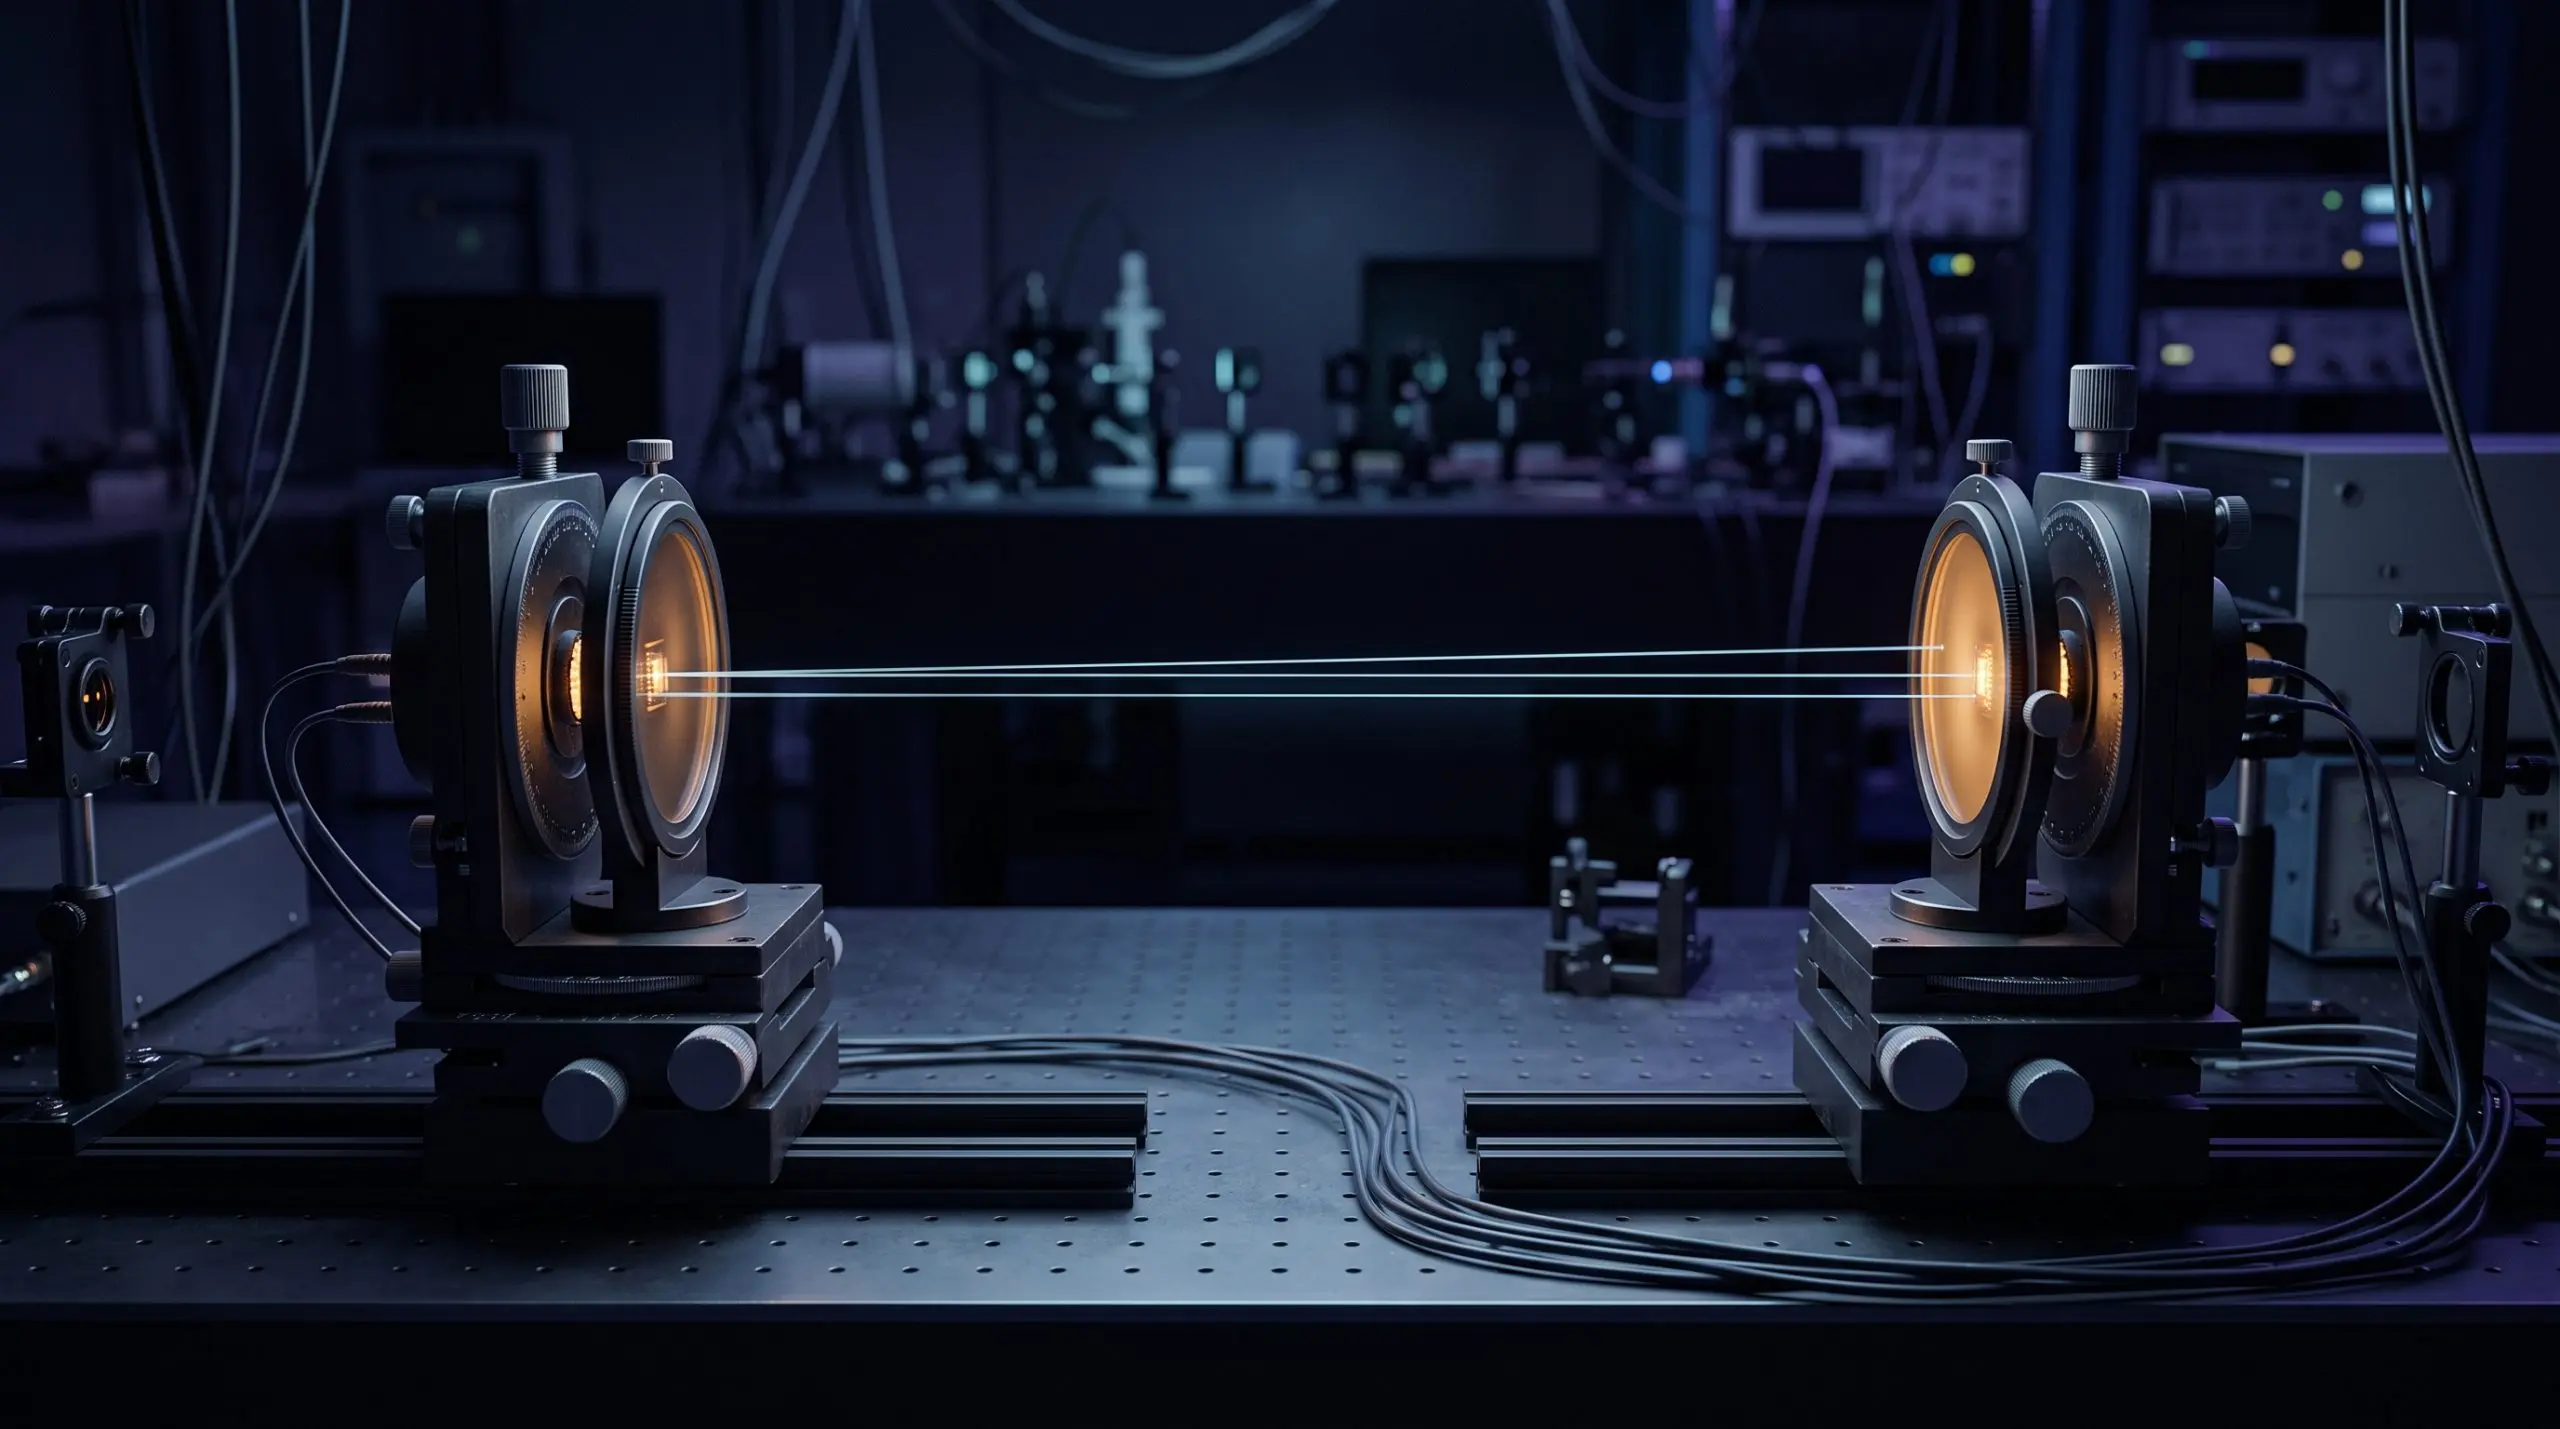
The work, demonstrated on the university’s 10-kWth PUR-1 research reactor, establishes verified bounds for integrating quantum cybersecurity into functioning industrial architectures. The team’s model reveals a trade-off between distance and responsiveness; achieving secure key exchange at 120 kilometers with a 20 Hz sampling rate requires a minimum of 24 minutes of lead time. These results provide a foundation for designing quantum-resilient communication frameworks for safety-critical systems like advanced reactors and microgrids.
A microreactor plant operating at just 2 MWe could supply the daily electrical and space heating needs of 2000 households and could produce process heat (675 °C) for seawater desalination, hydrogen production, fracking, heavy crude oil cracking, and many other applications. While these architectures would offer numerous advantages, they could be vulnerable to cyber attacks.
Phase-Encoding BB84 QKD System for Reactor Control
Purdue University’s 10-kWth PUR-1 research reactor served as the proving ground for a newly validated model linking quantum key distribution to the demands of real-time industrial control, moving beyond theoretical simulations to a functioning system. The reactor’s fully digital instrumentation and controls, uniquely licensed by the US NRC, allowed researchers to experimentally verify the bounds of integrating quantum cybersecurity into a safety-critical architecture. The work introduces three key parameters for evaluating quantum-secured industrial control: dynamic key pool size, QKD lead time and post-failure uptime, each directly linked to deterministic control system demands.
Dynamic key pool size represents the locally stored secret bits generated by the QKD link at each communication endpoint, while QKD lead time defines the minimum pre-operation duration needed to establish a self-sustained key reserve. Analysis revealed a trade-off between these factors and achievable communication distance, a critical consideration for maintaining continuous, quantum-secure communication.
The evaluation of post-failure uptime quantified system autonomy during QKD link outages, enabling predictive estimation of secure operation windows under various encryption schemes. Experiments at PUR-1 confirmed that real-time encryption and decryption of reactor signals could be sustained while adhering to strict nuclear operational timing requirements, a feat previously unproven in a live reactor environment. The results verified that quantum-secure communication can be embedded directly within a live reactor instrumentation and control system, achieving deterministic performance compatible with nuclear operational constraints.
Specifically, the system maintained control signal latency of under 10 minutes at a maximum distance of 95 kilometers, regardless of the number of signals being transmitted. The team’s model also highlighted a significant delay trade-off when prioritizing distance over responsiveness. The researchers state, establishing a foundation for integrating quantum-resilient security in autonomous nuclear plants.
The work expands upon previous demonstrations of QKD at PUR-1, confirming the ability to implement quantum communication for secure reactor remote operations. The study’s findings demonstrate the feasibility of maintaining continuous, quantum-secure communication within a live safety-critical system, a key step towards bolstering the resilience of industrial control systems against evolving cyber threats. The model and experimental results provide a quantifiable framework for assessing the performance of QKD in demanding environments. The work confirms that quantum-secure communication can be integrated into existing industrial control architectures without compromising operational safety or efficiency.
PUR-1 Reactor Demonstrates 95km Quantum Communication Limit
This work moves beyond theoretical simulations by demonstrating a functioning system capable of maintaining secure communication during live reactor operations, a step toward autonomous nuclear plants. Researchers evaluated the evolution of the key pool under continuous operation, establishing a relationship between key generation and consumption rates. This analysis focused on three specific metrics: the dynamic key pool size, the initial lead time needed for self-sustained operation, and the post-failure uptime, which measures secure communication duration following a quantum key distribution (QKD) outage.
The prototypic QKD testbed, integrated with the PUR-1 reactor, was used to gather data for these metrics, building upon previous work with a Toshiba Long-Distance QKD system. “The model links the stochastic nature of quantum key generation to deterministic control system demands,” the researchers state, introducing measurable quantities for evaluating system performance.
Dynamic Key Pool Size, Lead Time, and Uptime Metrics
Quantitative analysis at Purdue University links quantum key distribution performance directly to the demands of industrial control systems, revealing specific operational boundaries for secure communication. The work establishes that for the most demanding configuration, 20 Hz sampling at 120 km, QKD coupled with AES-256 encryption required a minimum of 24 minutes lead time, while distances below 95 km required less than 10 minutes, regardless of the number of signals transmitted, highlighting a trade-off between responsiveness and range.
A key request occurs periodically, dictated by the data sampling and reporting rate, while key generation intervals are typically longer than the data reporting period. The dynamic key pool size evolves based on unique-key demand for each communication cycle, allowing for predictive planning for resilient operation. “Reversing this analysis allows one to specify a desired uptime and compute the required lead time,” the researchers wrote, enabling proactive management of quantum resources.
This integration achieves deterministic performance compatible with the stringent constraints of nuclear operations, moving beyond theoretical models to a functioning system. The model accounts for the QKD lead time, representing the initial reserve needed for self-sustained operation, and the dynamic pool size, which evolves as keys are generated and consumed.
In the event of an optical link failure or interruption, the stored key reserve allows continued secure operation, with the duration dependent on pool size and ongoing consumption. Researchers explicitly accounted for this dynamic, deriving parameters to assess the system’s resilience to outages and ensure uninterrupted secure communication.
SKR and QBER Link QKD to Control System Demands
Beyond this distance, the time required for secure key exchange increases significantly, impacting the responsiveness of safety-critical systems like nuclear reactors. This finding stems from an experimental setup integrated directly into the university’s 10-kWth PUR-1 research reactor, providing data from a functioning industrial control architecture rather than solely theoretical models. The study quantified the relationship between key QKD metrics, secret key rate (SKR) and quantum bit-error-rate (QBER), and the specific communication needs of industrial control systems, including data sampling rates and reporting frequencies.
This lead time represents the initial reserve of keys needed to ensure continuous operation, highlighting a trade-off between distance and responsiveness when prioritizing quantum security. These parameters are important for evaluating the system’s ability to maintain continuous, secure operation even in the event of optical link failures or interruptions.
Quantum Key Distribution’s Information-Theoretic Security
Quantum Key Distribution (QKD) offers a path toward long-term confidentiality and autonomy for critical communications by bypassing reliance on computational assumptions, a necessity as quantum computers advance. The technology uses quantum mechanics to generate and distribute truly random symmetric keys, providing information-theoretic security independent of computational hardness, and multiple protocols, including BB84, entanglement-based and continuous-variable QKD, have been developed to achieve this. Following key distillation, both communicating parties possess identical, quantum-random bit strings suitable for use with symmetric One-Time Pad (OTP) encryption, achieving unconditional security.
The fundamental security of QKD stems from quantum physical laws, specifically the no-cloning theorem and Heisenberg’s uncertainty principle. Any attempt to intercept photons disturbs their quantum states, introducing measurable errors detectable by legitimate users. Purdue University researchers integrated QKD within digital control networks to provide continuous, verifiable key rates for data streams associated with sensing, control, and supervisory communication, even under potential adversarial activity.
A detailed mathematical formulation of the framework developed by the team accounts for the coupling of key generation and distribution systems, with the key generation system contributing newly distilled symmetric keys to a shared reserve pool. This process is stochastic, with fluctuations in both the size of generated bitstreams and computational security, and the team’s model demonstrates that AES-256 encryption can extend the maximum secure operation distance when quantum key generation is limited, though at the expense of information-theoretic security.
Although the analysis assumes all encryption key material is generated after the QKD system is operational, the model allows for specification of a desired uptime and computation of the required lead time for key generation.
Microreactor Applications and Vulnerability to Cyber Attacks
Microreactor deployments, particularly in remote locations, face escalating electricity costs beyond fuel and renewable variability. Transportation expenses for fuel over difficult terrain contribute significantly to these burdens. Traditional encryption methods, reliant on mathematical complexity, are increasingly threatened by advances in computing, including the potential of quantum computers to break them. Existing QKD architectures, designed for uninterrupted key distribution even under attack, have not fully addressed the critical issue of smart grid key management, and decentralized key management frameworks, though demonstrating high availability, can be hampered by network latency.
The Purdue University team addressed this gap by experimentally integrating QKD within the digital control networks of a functioning 10-kWth PUR-1 research reactor, moving beyond purely theoretical evaluations. The team’s key distribution system draws from a generated pool of keys, supplying encryption applications at intervals aligned with the reactor’s operational cycle and data exchange rate.
These results establish a quantifiable relationship between communication distance and key availability, a key factor for maintaining continuous, verifiable security in safety-critical systems. AES-256 encryption was also evaluated as an alternative for higher data rates and extended distances, with the implementation refreshing the 256-bit key and 128-bit initialization vector with each data exchange cycle using QKD-generated bitstreams. The study’s findings highlight the need for dedicated, cybersecurity-integrated communication channels for remote reactor operations, a field previously limited to preliminary feasibility studies and monitoring scenarios.

See today’s quantum computing news on Quantum Zeitgeist for the latest breakthroughs in qubits, hardware, algorithms, and industry deals.